

Vami Research: secure AI agents, demonstrable compliance
Vami Research brings together the research, analysis, and knowledge work of VamiSec GmbH. We investigate how AI agents are attacked, tested, and secured, and how regulation can be implemented as an engineering task. The results feed into knowledge pages, whitepapers, tools, the Vami solutions, and our consulting.
Investigate. Verify. Operationalize.
We evaluate primary sources and incidents, check claims against threat models, tests, and experiments, and make the results usable: as knowledge pages, whitepapers, tools, solutions, or consulting.
- 01
Investigate
We evaluate standards, regulation, advisories, and technical literature at the primary source wherever possible and label secondary sources. In doing so, we separate what is mandatory, what is considered proven practice, and what we recommend.
- 02
Verify
We check claims against threat models, tests, and experiments — for our ICSPIS 2026 paper, for example, across 3,024 profile-fault-trace cells. Where standards or tools reach their limits, we say so openly.
- 03
Operationalize
Findings flow into knowledge pages, whitepapers, and interactive tools, into the Vami solutions, and into our consulting: to where they take effect in projects, audits, and pipelines.
Tampered Claude Code extension: from incident to step-by-step checks
On October 29, 2026, the marketplace of the AI code editor Cursor distributed tampered versions of the Claude Code extension under the genuine identifier. The malicious code added an attacker SSH key, set up persistence, and transmitted a profile of the machine. Based on Cursor's security notice and further analyses, we have set out how to check whether you are affected, clean up, rotate credentials, and assess reporting obligations — and why uninstalling alone is not enough.
What we have published recently
Threat briefings, deep dives, talks, events, and expert articles from all research areas, sorted by date and filterable by topic.
The agentic stack, researched layer by layer
Agentic systems connect the model, orchestration, tools, identities, supply chain, testing, and governance. For each layer, we show the open question from practice, our approach, and the pages where you can dig deeper.
Research question
How do you prevent inputs from steering a model or confidential data from ending up in prompts?
Our approach
As things stand today, prompt injection cannot be fully prevented. We rely on limited permissions, input and output filters, and approvals for critical actions, and map findings to the OWASP Top 10 for LLM Applications. VamiGuard detects sensitive data in prompts locally in the browser, pattern-based and without a guarantee of completeness.
Read more
Research question
How does an agent stay on task when content, memory, or other agents try to divert it?
Our approach
We secure agents along the OWASP Top 10 for Agentic Applications, from Agent Goal Hijack to Rogue Agents, following the principle of Least Agency. At runtime, we draw on the OWASP Agent Control Standard, an early specification (v0.1.0): a Guardian checks actions at defined hooks. ISO/IEC 27090 describes AI-specific attacks along the lifecycle but touches on agents only in passing.
Read more
Research question
Which tools may an agent use, and how do you recognize manipulated tool descriptions or skills?
Our approach
We treat MCP servers and Agent Skills like privileged software: review, sandboxing, and allowlisting before deployment, signed tool manifests with version pinning, and an inventory in operation. We map risks to the OWASP MCP Top 10 (v0.1, Beta) and model trust boundaries with STRIDE and MAESTRO.
Read more
Research question
Whose permissions does an agent act with, and how do you prevent it from using them beyond its task?
Our approach
A manipulated agent does not break in; it uses legitimate permissions. That is why we apply Zero Trust to agents: a separate identity per agent, short-lived, tightly scoped tokens, and authorization per action instead of per session. We test MCP authorization against OAuth 2.1 with audience binding and the token passthrough ban.
Read more
Research question
Where do the packages, models, and code that coding agents suggest or install come from, and who checks them?
Our approach
AI models suggest packages that do not exist, and attackers can register exactly those names. We secure coding agents and their harness in five protection layers, document models and datasets as an AI-SBOM, and put LLM triage on top of deterministic SAST, not in its place.
Read more
Research question
How do you prove that controls for agents take effect, and not just that events were logged?
Our approach
We derive tests from the threat model: MAESTRO and STRIDE provide boundaries and invariants, and an Evidence Contract defines the required telemetry. In the ICSPIS 2026 paper, security-relevant bindings raised recall from 16.7% to 92.9%. VamiRedteam checks every agent action against the authorized scope before execution.
Read more
Research question
Who is accountable for an AI agent, and how do you demonstrate governance without maintaining documents twice?
Our approach
We integrate the AI management system under ISO/IEC 42001 into the existing ISMS instead of running it alongside, and put obligations into context, such as the AI Act transparency obligations that have applied since August 2, 2026. VamiGRC maintains five management systems on one GRC graph; autonomy levels L0–L3 determine what requires approval.
Read more
GRC becomes an engineering discipline
Agentic GRC Engineering combines machine-readable frameworks, a shared GRC graph, and AI agents that work according to your approval rules. Instead of more stacks of documents, this creates connections and evidence that stand up to an audit.
- 01Frameworks as CodeWith OSCAL, frameworks become data: every control is an addressable object, and version changes become diffs. Since OSCAL 1.2.0, mappings between frameworks have been part of the standard — implement once, comply many times.
- 02One GRC graph, five management systemsThe Harmonized Structure gives management system standards the same clause structure. In VamiGRC, ISMS, PIMS, AIMS, CSMS, and BCMS share the same assets, suppliers, risks, and evidence on one GRC graph.
- 03Agents with guardrailsVamiAI answers questions from the integrated management system with source references, and on request also in Microsoft Teams. Autonomy levels L0 to L3 determine what an agent may handle on its own and what requires approval.
- 04Interfaces & integrationImport your own frameworks as OSCAL in JSON, XML, or YAML; export the control catalog, Statement of Applicability, and assessment results as OSCAL. Launch automated pentests in VamiRedteam directly from VamiGRC.
- 05Evidence & trustOur own Trust Center, “Powered by VamiGRC,” shows the principle: ISO/IEC 27001 certificate, policies for download, Statements of Applicability on request. VamiGRC answers customer questionnaires with evidence for every response; your team reviews and approves.
See it live: VamiGRC Christmas Bootcamp “Agentic GRC Engineering” on December 12, 2026, in Sankt Augustin and via livestream on LinkedIn and YouTube, free of charge.
Our research areas, focused on agentic AI
The first group is dedicated to agentic systems and the question of how AI is changing security work. The second covers the security and compliance foundations on which these systems run.
Agentic Research
How AI agents are secured, tested, and governed, and how AI is changing security work itself: from pentesting through threat modeling and code analysis to reverse engineering and GRC.
Security & compliance research
Supply chain, threat landscape, product and OT security, cloud sovereignty, regulation, and post-quantum cryptography: the foundations on which agentic systems run.
From research area to solution
The Vami solutions bring the topics of our research areas into operation. Each solution can be used on its own; for each one, you can see which research areas feed into it. The hosted solutions run on T Cloud Public, exclusively in German data centers.
 VamiGRCAgentic Integrated Management System
Fed byAgentic GRC EngineeringProduct, OT, Automotive & MedTech SecurityRegulatory Intelligence
 VamiAppSecSecure SDLC & Product Security Compliance (opens external website)
Fed byAI Code Security & Coding AgentsSoftware & AI Supply ChainProduct, OT, Automotive & MedTech Security
 VamiThreatAI-Assisted Threat Modeling (opens external website)
Fed byAI Threat ModelingProduct, OT, Automotive & MedTech Security

 VamisetAsset Discovery & Compliance Checks (opens external website)
Fed byAgentic GRC EngineeringThreat & Vulnerability IntelligenceCloud Security & Digital Sovereignty
Services that put findings into practice
GRC, IT Security, Agentic AI Security, Managed Services, and Trainings & Certifications: in these service areas, we support you from analysis through implementation to operation.
Shared openly: knowledge, tools, talks
We share what we develop: deep dives with source references and interactive self-checks are freely accessible, whitepapers are available free of charge via a form, and in talks we put our results up for discussion.
Five topic areas from GRC to Secure Software & Product Development, each with deep dives, sources, and in-depth pages.
CISO whitepapers, Reality Checks, and our Research Edition: free of charge, each with a download form on its own page or in the related deep dive.
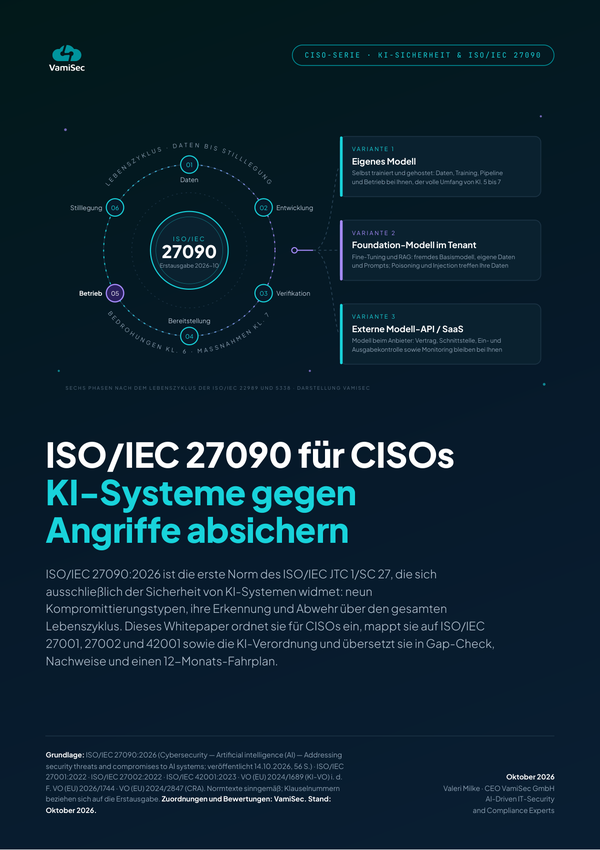 ISO/IEC 27090 for CISOs — securing AI systems against attacks
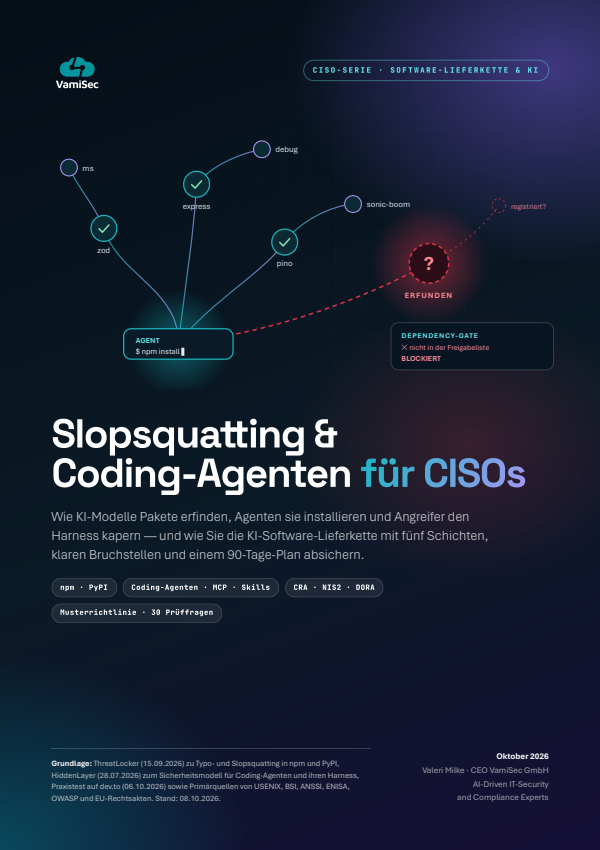 Slopsquatting & Coding-Agenten für CISOs — securing the AI software supply chain
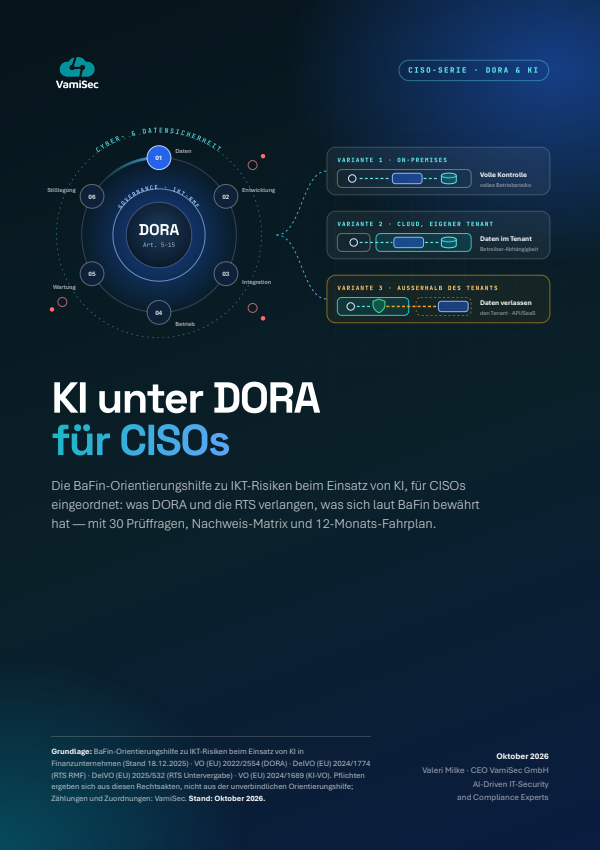 KI unter DORA für CISOs — BaFin guidance on ICT risks
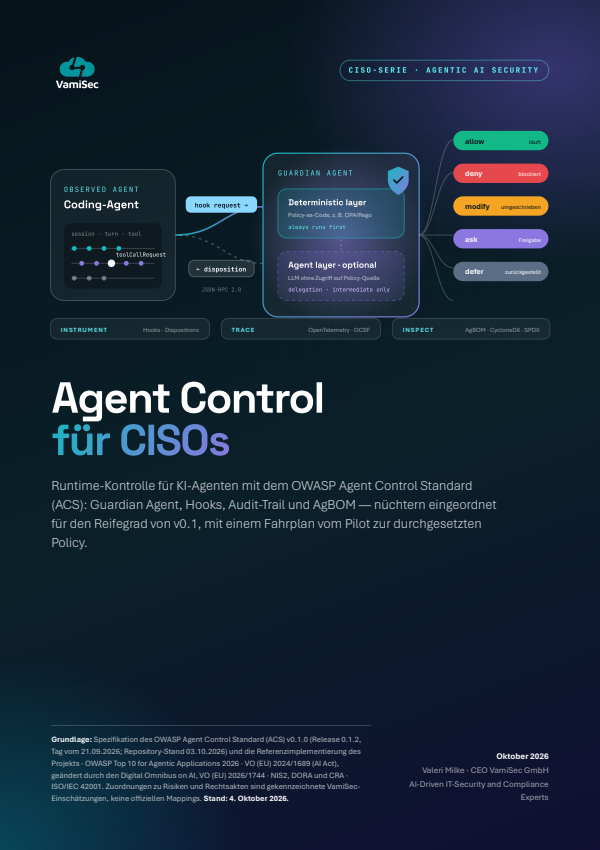 Agent Control for CISOs — OWASP Agent Control Standard (ACS)
 Threat-Model-Guided Security Testing for Agentic AI — Research Edition
 Third-Party Risk für CISOs — EBA Non-ICT Guidelines 2026
 Automotive Threat Matrix — ATT&CK for Vehicles
 AI Act Reality Check — High-Risk Deadlines, GPAI & Agentic AI
Self-checks, navigators, simulators, and checkers on our knowledge pages show where you stand and what the next step is. There is also VamiGuard, our free browser extension for data protection in AI prompts.
Where we present results and put them up for discussion: conference talks, events, and expert articles, for example in the trade journal mt|medizintechnik.
Research Edition and CISO whitepapers
Work on core questions of AI security: telemetry that makes agents testable, runtime control under the OWASP Agent Control Standard, the new ISO/IEC 27090, and the supply chain of coding agents.
Research EditionAgentic Offensive SecurityThreat-Model-Guided Security Testing for Agentic AI — Research EditionBy Valeri Milke · October 4, 2026Agentic AI SecurityAgent Control for CISOs — OWASP Agent Control Standard (ACS)By Valeri Milke · October 4, 2026Agentic AI SecurityISO/IEC 27090 for CISOs — securing AI systems against attacksBy Valeri Milke · October 22, 2026AI Code Security & Coding AgentsSlopsquatting & Coding-Agenten für CISOs — securing the AI software supply chainBy Valeri Milke · October 8, 2026At a glance
The figures are calculated automatically from the published content, so they stay up to date.
- Research areas
- 12
- Deep Dives
- 89
- Whitepapers
- 23
- Interactive tools
- 13
- Vami solutions
- 9
- Languages
- 5
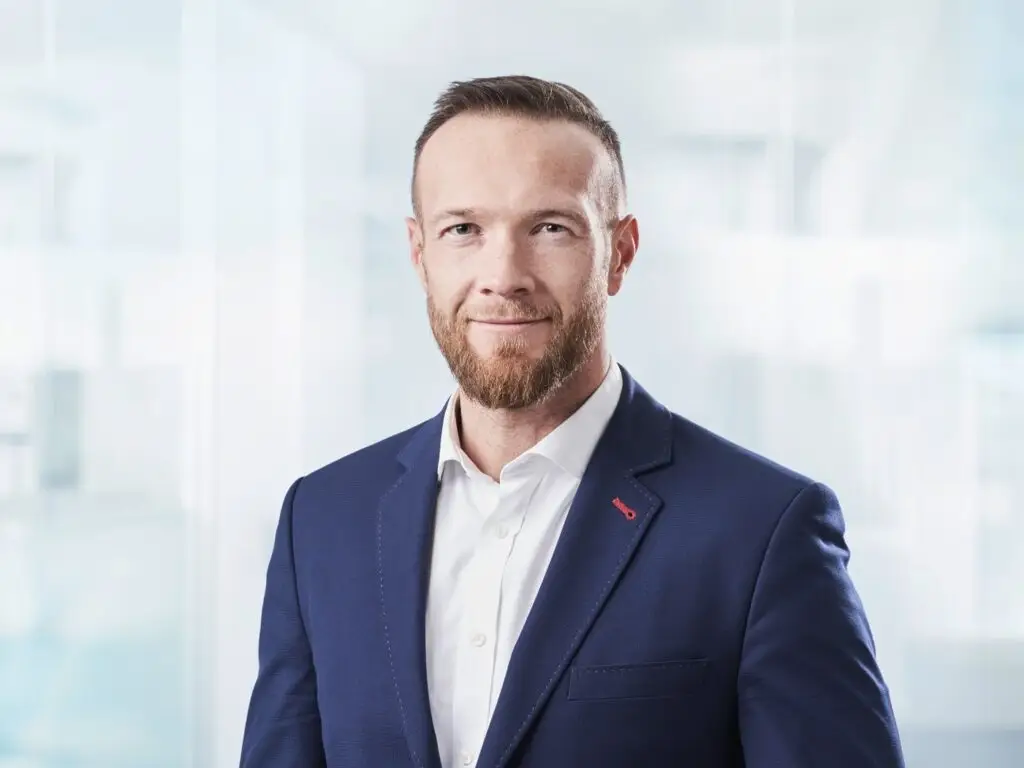
Valeri Milke
Managing Director, VamiSec GmbH · ISO 27001 & ISO 42001 Lead Auditor
LinkedIn (opens external website)Founder-led and grounded in practice
Vami Research is not a separate institute but the research, analysis, and knowledge work of VamiSec GmbH in Bonn, founded in 2025. Its roots go back to 2009, to SoftSCheck, a research project on threat modeling and fuzzing at Bonn-Rhein-Sieg University of Applied Sciences, funded by the German Federal Ministry of Education and Research (BMBF). Vami Research is led by founder and managing director Valeri Milke. Our publications grow out of consulting, testing, and audits and feed back into them.
View open positionsFound a vulnerability?
Please report security vulnerabilities in our websites or solutions to security@vamisec.com. This contact is also listed in our security.txt; reports are welcome in German or English.
Report a vulnerabilityFrequently asked questions about Vami Research
What Vami Research is, how we work, and how you can work with us.
What is Vami Research?
Vami Research is the name for the research, analysis, and knowledge work of VamiSec GmbH, not a separate company. It includes deep dives, whitepapers, threat briefings, interactive tools, talks, and expert articles. The focus is on agentic AI systems, complemented by the supply chain, the threat landscape, regulation, product and cloud security, and post-quantum cryptography.
What does Agentic GRC Engineering mean?
GRC becomes an engineering discipline: frameworks are available in machine-readable form, for example as OSCAL catalogs, management systems share a GRC graph, and AI agents handle routine work according to defined approval rules. In VamiGRC, autonomy levels from L0 to L3 determine what requires approval. The goal is evidence that stands up to an audit.
How does Vami Research handle new vulnerabilities and incidents?
Our focus is timely analysis and assessment. PHP2Shell and Brotli2Shell were found and disclosed by others; the tampered Claude Code extension was reported by Cursor. For each of them, we published threat briefings with checks and measures. We accept reports of vulnerabilities in our own systems at security@vamisec.com.
How do findings feed into the Vami solutions?
Research areas and solutions work on the same questions: OSCAL is the backbone of VamiGRC, VamiThreat models agentic AI systems using MAESTRO, and VamiRedteam checks every agent action against the authorized scope before execution. On each research area page, you can see which solutions and services the area feeds.
How up to date is the content?
Our deep dives state their as-of date as well as the underlying standards and sources. We publish threat briefings promptly, for example on October 31, 2026, covering the tampering of the Claude Code extension on October 29, 2026. Our content is created in part with AI support, so please verify critical details before implementing them.
How do you work with companies and the expert community?
We support companies with consulting, testing, audits, and managed services, starting with an initial consultation. We present results for discussion in trade media and at conferences, for example in the trade journal mt|medizintechnik. Talks have been accepted at DevFest Nairobi 2026, ICSPIS 2026 in Dubai, and CyberWiseCon Europe 2027 in Riga.
Does Vami Research also publish academic work?
Yes. The paper “Threat-Model-Guided Security Testing for Agentic AI: MCP Traces with MAESTRO and STRIDE” by Valeri Milke was accepted for ICSPIS 2026 (IEEE), the 9th International Conference on Signal Processing and Information Security, taking place from November 10 to 12, 2026, in Dubai. The Research Edition with the accepted version and an ACS Practitioner Brief is available free of charge.
From research to security in operation
Talk to us about your AI agents, your regulatory requirements, or your supply chain. In an initial consultation, we clarify which findings, tools, and solutions fit your situation.