
VamiSec speaks at International Cyber Expo 2026 in London: Agentic AI Risk Assessment with MAESTRO and AI Red Teaming
September 22, 2026
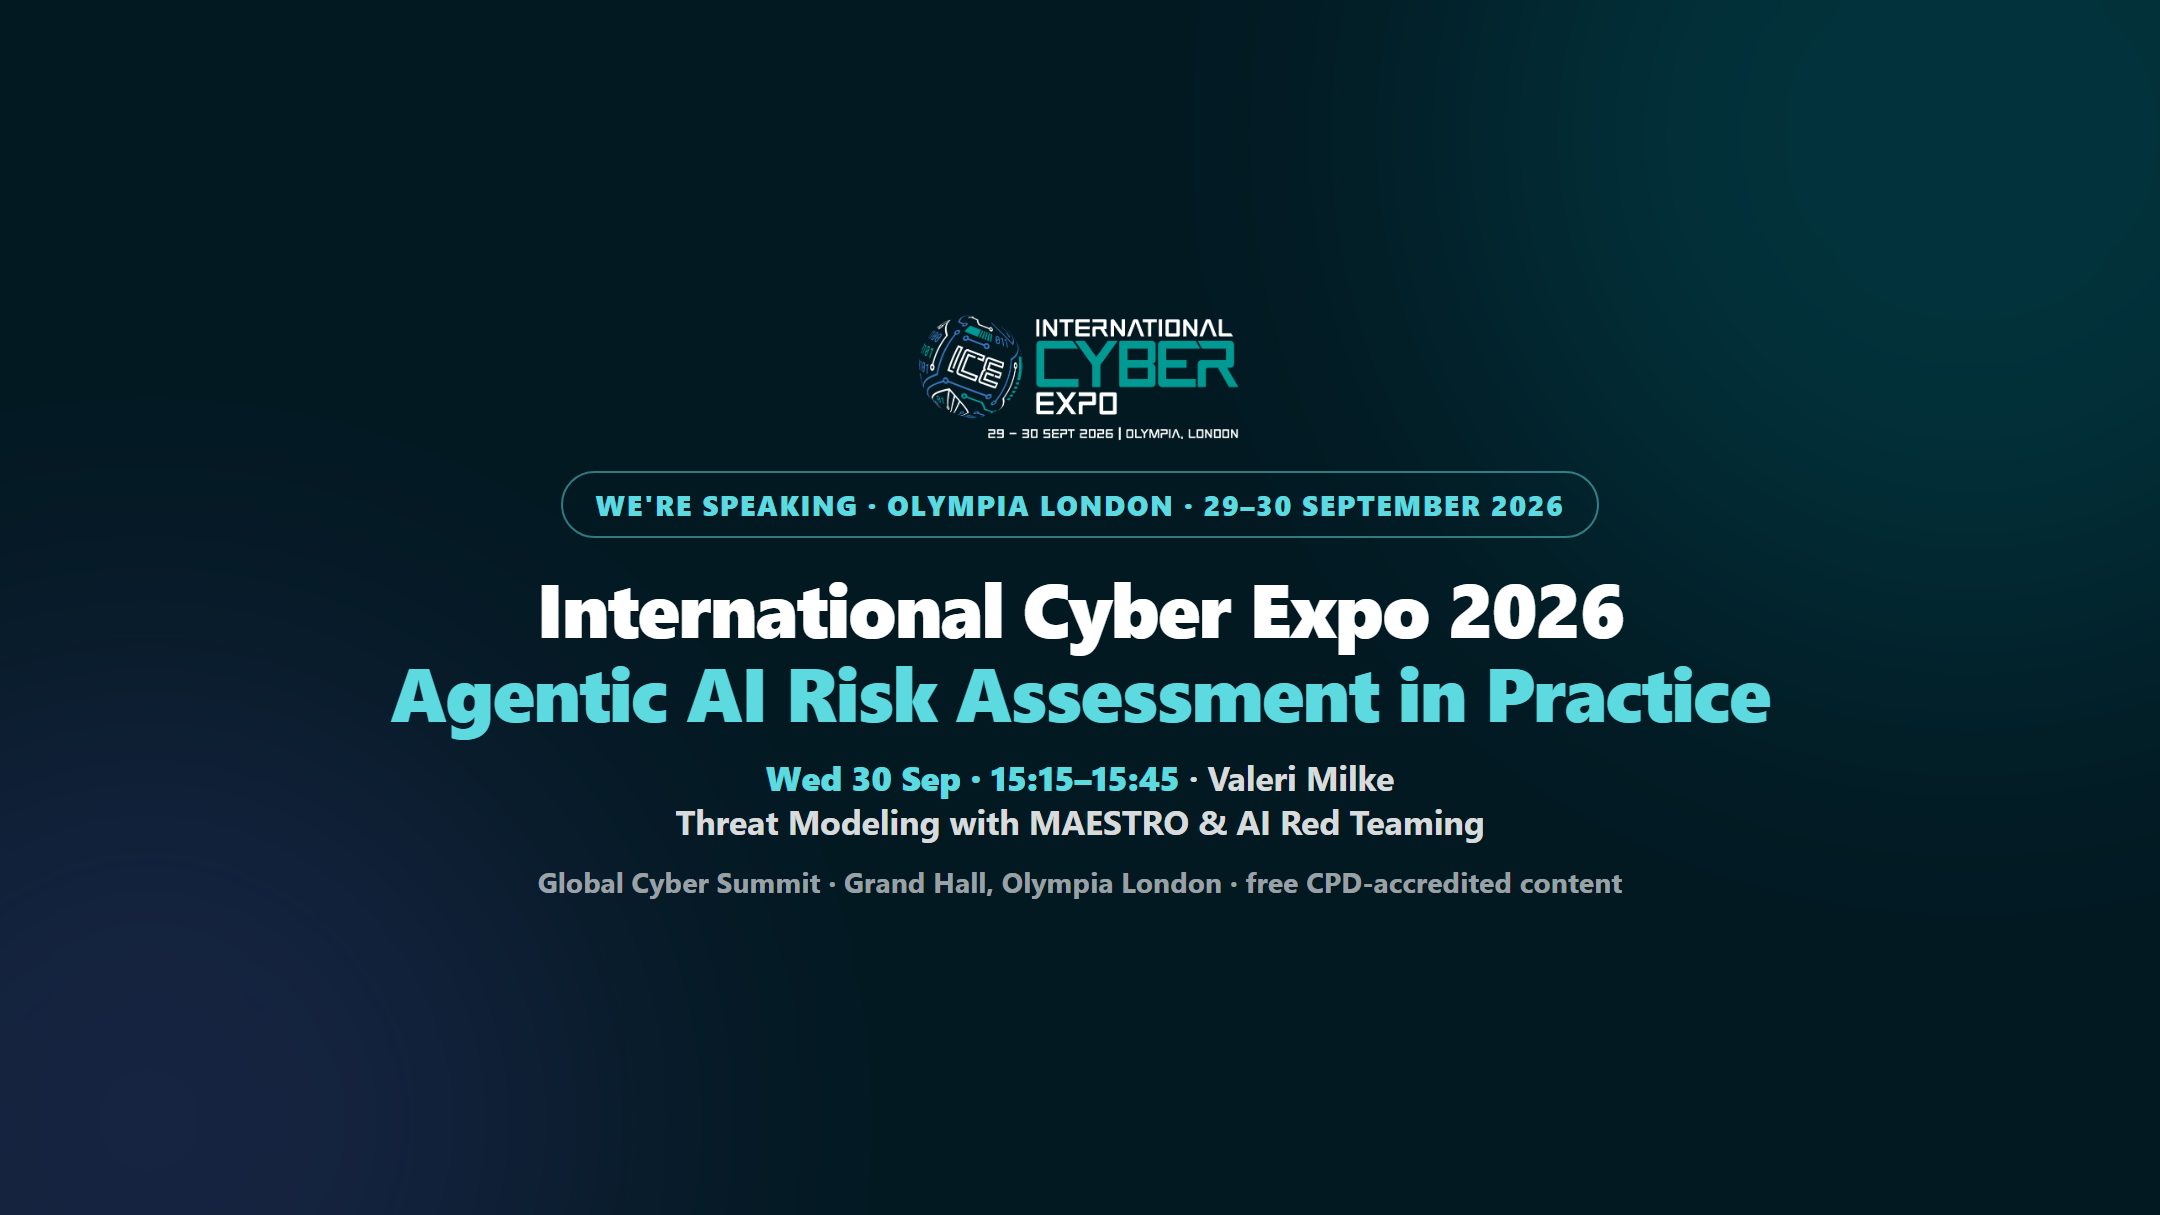
VamiSec on the summit stage: our speaking slot in London
International Cyber Expo 2026 is putting VamiSec on stage: on Wednesday, 30 September 2026, CEO Valeri Milke speaks from 15:15 to 15:45 (London time) at the Global Cyber Summit — the topic: “Agentic AI Risk Assessment in Practice: Threat Modeling with MAESTRO and AI Red Teaming”. The setting is the Grand Hall at Olympia London; organiser Nineteen Group expects, by its own figures, more than 100 exhibiting companies, over 7,500 trade visitors from more than 90 countries and a conference programme with over 100 speakers. Entry is free after registration — including the full CPD-accredited programme.
The International Cyber Expo: London's cybersecurity meeting point
Under the banner “Uniting Global Innovation For The Next Era Of Cybersecurity”, International Cyber Expo brings vendor innovation, government and practitioner experience together in Kensington on 29 and 30 September 2026 (Tue 09:30–17:30, Wed 09:30–16:00). The same pass also opens the co-located International Security Expo with over 300 exhibiting brands — according to the organiser, the only privately run security event fully backed by the UK Government, from the Home Office and JSaRC to DBT and SIA. Add to that a Government Zone, pavilions from IASME, ADS & techUK and DSIT, a live demonstration of an attack on a data centre running several times daily (staged with CrisisCast and involving Fortinet, Tenable and CrowdStrike), Cyber Griffin demos by the City of London Police — and, to close day 1, an open networking drinks reception.
Global Cyber Summit: the heart of the conference
The Global Cyber Summit is the event's high-level stage: more than 30 sessions across two days, CPD-accredited in partnership with The CPD Group and The Security Institute. The speaker line-up includes voices from ING, the City of London Police, NHS England, Huntress and Rootshell Security. The 2026 agenda reads like a CISO's risk register: AI and quantum, geopolitics in a fractured world, cyber-enabled fraud, supply chain vulnerability, the skills gap, ransomware and the protection of critical national infrastructure.
Our topic: once AI agents act, classic threat modelling is no longer enough
Agentic AI systems plan, use tools, remember intermediate state and make decisions — and that shifts the attack surface fundamentally. If you only secure prompts and models, you miss what happens between autonomy, tool access, persistent memory and blurred control boundaries: a compromised agent does not escalate like a script, it escalates like an employee with system access. This is exactly where MAESTRO comes in — a threat modelling framework built specifically for multi-agent environments that works systematically through the layers of agentic systems where STRIDE and friends reach their limits.
The session: from MAESTRO threat models to controls that hold up
The 30 minutes are hands-on practice rather than slide rhetoric, built around four stations: first, the most dangerous agentic-AI risks, illustrated with real-world incidents. Second, threat modelling with MAESTRO across autonomy, tool use, memory and control boundaries. Third, the design and execution of AI red teaming scenarios aligned directly to the MAESTRO categories — so that what the model flags as critical is what actually gets tested. And fourth, the step where many programmes fail: translating red-team findings into risk assessments, mitigations and enterprise controls that stand up to audits and regulators.
Agentic AI is the leitmotif of this year's agenda
That our topic hits a nerve is evident from the summit agenda itself: in “We Gave AI a Penetration Testing Job. Here's What Happened”, Rootshell reports on an AI agent deployed in penetration testing; “No Hands on the Keyboard” asks about agentic AI and the limits of criminal law; another session investigates whether an AI agent really “broke free” and attacked another company; and “What Does Threat Modeling Solve for AI Security?” poses the methodology question. Our contribution supplies the end-to-end answer: a repeatable approach from threat model through red teaming to control catalogue.
The practice behind it: threat models, AI red teaming and governance from a single team
What fits into 30 minutes on stage is everyday project work for us: we model production agent architectures with STRIDE and MAESTRO, test AI systems through AI/LLM pentesting and red teaming, and translate the results into governance aligned with the EU AI Act, NIS2, DORA, the CRA and ISO/IEC 42001 — as an accreditation-experienced team built around an ISO 27001 and ISO 42001 lead auditor. How we set up AI threat modelling with MAESTRO: https://vamisec.com/en/ai-threat-modeling-maestro; our approach to agentic pentesting: https://vamisec.com/en/agentic-ai-pentesting.
Meet us in London — or afterwards
We are on site on both days of the event — before and after the Wednesday-afternoon talk, you will also find us around the Global Cyber Summit or at the networking reception closing day one. Write to us in advance at contact@vamisec.com if you would like to schedule a conversation about agentic-AI risks, threat modelling or AI governance. Can't make it to London? We will unpack the key takeaways from both days here on the blog afterwards — and four weeks later you can meet us in person at it-sa in Nuremberg: https://vamisec.com/en/it-sa-2026.
All links for the event
Event page & free registration: https://www.internationalcyberexpo.com/ · Session detail page for our talk: https://www.internationalcyberexpo.com/international-cyber-expo-2026-agenda/agentic-ai-risk-assessment-practice-threat-modeling-maestro-ai-red-teaming · Valeri Milke's speaker profile: https://www.internationalcyberexpo.com/speakers/valeri-milke · Global Cyber Summit agenda: https://www.internationalcyberexpo.com/global-cyber-summit · Venue & directions — Olympia London: https://www.internationalcyberexpo.com/when-where · Co-located International Security Expo: https://www.internationalcyberexpo.com/international-security-expo · AI threat modelling with MAESTRO at VamiSec: https://vamisec.com/en/ai-threat-modeling-maestro · Agentic AI pentesting at VamiSec: https://vamisec.com/en/agentic-ai-pentesting
Do you have questions about your organization's IT security?
Free Initial Consultation →