

Knowledge. Practice. Orientation.
Consulting portfolio, whitepapers, studies and practical guides on current security and compliance topics — concise, well-founded, ready to use.
Knowledge by topic
Our knowledge is organized into five topic areas. Each topic area has its own knowledge page with in-depth content, related pages and the matching whitepapers for download.
GRC – Governance, Risk & Compliance
ISO 27001, BSI IT-Grundschutz, DORA, NIS2, the EU CRA and the EU AI Act — governance, risk management and audit-ready compliance.
Explore topicIT Security
Penetration testing, secure coding, threat modeling and a secure SDLC — technical security across the entire lifecycle.
Explore topicAgentic AI Security
LLM & agentic-AI pentesting, prompt injection, OWASP LLM Top 10 and AI threat modeling — securing AI systems.
Explore topicCloud Security
CSPM & CNAPP (partner: Wiz), sovereign cloud architecture, BSI C5, ISO 27017 and the EU Cloud & AI Act (CADA) — cloud security, compliance and sovereignty as one.
Explore topicSecure Software & Product Development
Secure coding, SSDLC and supply chain security (SLSA, SBOM), plus product security by product type: CRA, IEC 62443, UN R155 and ISO/SAE 21434 for vehicles, MDR for medical devices.
Explore topicNews & pinned posts
Partnerships, milestones and new offerings — the most important posts from the VamiSec universe.
 Claude Code extension tampered with in the Cursor marketplace: what developer teams need to know about the SSH backdoorTampered versions of the Claude Code extension in the Cursor marketplace set up SSH backdoors on developer machines. We explain what the malicious code did, how to check whether you are affected and which steps are needed now.Read more →
 Brotli2Shell (CVE-2026-111497): What organizations need to know about Node2Shell and HTTP2Shell nowCritical flaw in Google's Brotli decoder: Node.js, .NET, Python, Bun, Envoy, Istio and many other products are affected. We explain the root cause, fixed versions, attack paths and current status, and show what organizations should do now.Read more →
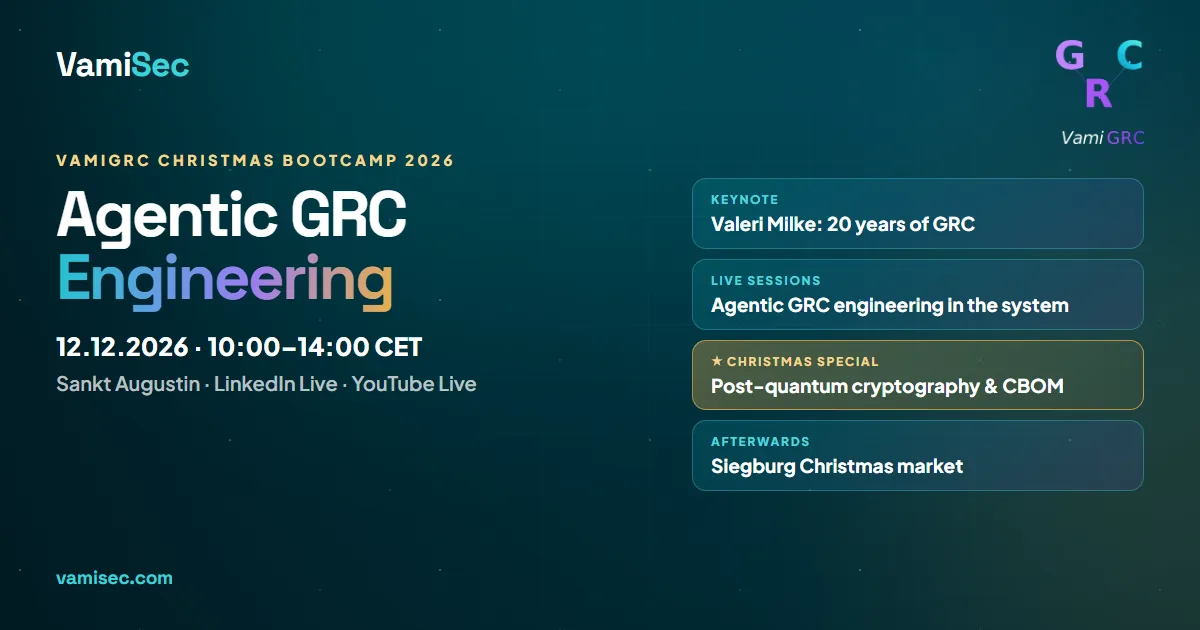 VamiGRC Christmas Bootcamp on 12 December: agentic GRC engineering – on site and liveOn Saturday, 12 December 2026, VamiSec invites you to the VamiGRC Christmas Bootcamp in Sankt Augustin near Bonn – on site or live on LinkedIn and YouTube. Valeri Milke and partners show how agentic GRC engineering makes NIS2, the CRA, the AI Act and supply chain risks manageable – plus a Christmas special on post-quantum cryptography and CBOM. Participation is free of charge.Read more →
 Expert article in mt|medizintechnik: maintaining connected medical devicesIn issue 4.2026 of the trade journal mt|medizintechnik, Valeri Milke explains why vulnerability and patch management for connected medical devices are a matter of patient safety. Our new knowledge page summarises his key points and explores them in depth.Read more →
 Expert article in mt|medizintechnik: risk management for AI systems in clinical settingsIn issue 2.2026 of the trade journal mt|medizintechnik, Valeri Milke shows how hospitals can use risk management to safeguard their use of AI systems. Our new knowledge page summarises his key points, updates them and explores them in depth.Read more →
 BaFin AI Guidance: What Banks and Insurers Should Now Implement for ICT Risks under DORAOn 18 December 2025, BaFin published its guidance on ICT risks in the use of AI. It is non-binding, but across 38 pages it shows how financial entities can apply DORA’s requirements to AI systems — from governance through testing and cloud contracts to incident reporting. We have analyzed it and published an interactive knowledge page plus a CISO whitepaper.Read more →
 EBA Guidelines on Third-Party Risk 2026: What Financial Entities Now Need to Know about Non-ICT Service ProvidersOn 18 September 2026 the EBA replaced its 2019 Outsourcing Guidelines with EBA/GL/2026/09. Every recurring non-ICT service that supports a function now falls within a DORA-consistent framework — complete with a register, a catalogue of contractual clauses, subcontracting rules and a two-year transitional period. We have worked through the Final Report and published an interactive knowledge page together with a CISO whitepaper.Read more →
 MID-Digitale Sicherheit: 50% grant for pentests, training & baseline IT protectionNew overview page: the NRW programme funds IT security measures with a 50% grant (€4,000–15,000) — from as-is analysis with penetration testing to security training and the initial purchase of hardware & software. Awarded in a monthly lottery via NRW.BANK — we support you from expression of interest to proof of use.Read more →MID-Digitalisierung: 50% grant for developing digital productsThe NRW programme funds external services for developing marketable digital products built on key technologies such as AI with a 50% grant (€4,000–15,000), awarded in a monthly lottery. VamiSec develops as your contractor with security by design plus CRA and AI Act conformity from the first sprint.Read more →Up to €15,000 in grants: GRC consulting via MID-Digitale Prozesse (NRW)The NRW state programme “Mittelstand Innovativ & Digital” funds external consulting for digitalising your GRC processes — from NIS2, CRA, EU AI Act and ISO 27001 gap analyses to roadmap, tool selection and VamiGRC implementation. The grant can cover up to 100% of the consulting. 2026 call: applications from 7 Sep to 1 Dec 2026 via NRW.BANK — we guide you through the entire funding process.Read more →
 VamiSec is a member of the Wiz Partner Alliance in EMEA — with Technical Foundations and Demo AccreditationVamiSec GmbH is a member of the Wiz Partner Alliance for the EMEA region — listed in the Wiz Partner Alliance Directory and holding the Wiz Partner Technical Foundations Badge as well as the Wiz Partner Demo Accreditation.Read more →VamiSec and softScheck — strategy meets technical depthValeri Milke also takes on the role of Managing Director at softScheck GmbH. VamiSec remains the strategic home for GRC, compliance, and management systems — complemented by softScheck’s 20+ years of product security expertise (threat modeling, pentest, SSDLC, fuzzing).Read more →
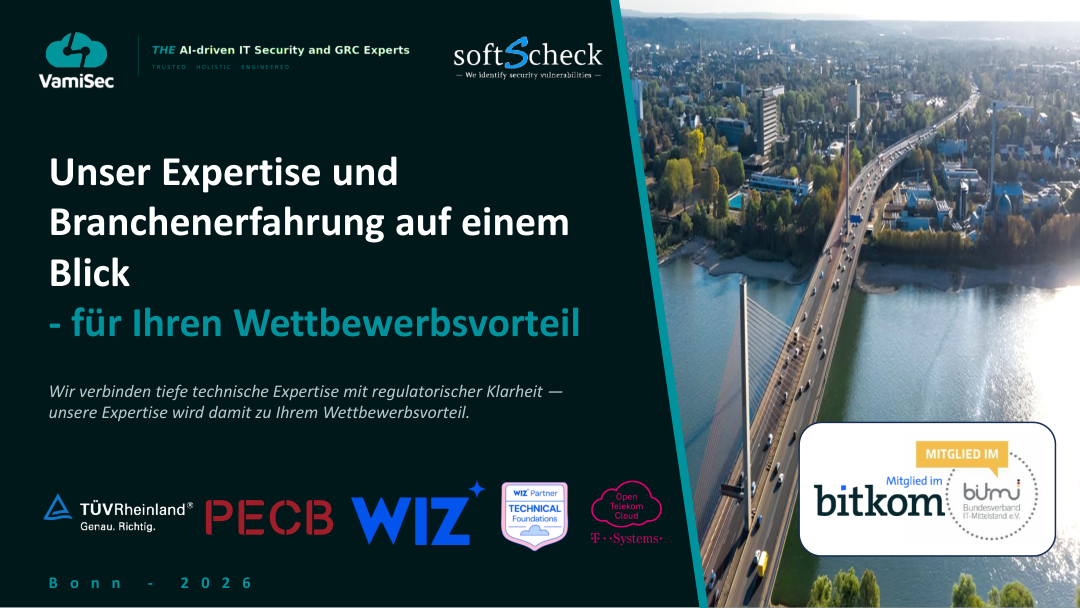
VamiSec Consulting Portfolio 2026
Trusted · Holistic · Engineered
Our complete service portfolio in one deck — from ISO 27001, NIS2, DORA and CRA to IT- & Cloud Security, AI Governance, Managed Services and the Vami IMS Framework. 27 pages, compact.
All whitepapers at a glance
Hands-on whitepapers from our consulting work — each with its own page and direct download form, sorted by our five knowledge areas.
 GRC – Governance, Risk & ComplianceTLPT per DORA: How to Truly Protect Your Crown JewelsView whitepaper page →
 GRC – Governance, Risk & ComplianceISO 27001 and IT-Grundschutz Combined — A Practical WorkflowView whitepaper page →
 GRC – Governance, Risk & ComplianceCRA Reality Check — Zero-Days, Supply Chain & AIView whitepaper page →
 GRC – Governance, Risk & ComplianceDORA Reality Check — Third-Party Risk & Agentic AIView whitepaper page →
 GRC – Governance, Risk & ComplianceNIS2 Reality Check — Registration, Supply Chain & LiabilityView whitepaper page →
 GRC – Governance, Risk & ComplianceAI Act Reality Check — High-Risk Deadlines, GPAI & Agentic AIView whitepaper page →
 GRC – Governance, Risk & ComplianceThird-Party Risk für CISOs — EBA Non-ICT Guidelines 2026View whitepaper page →
 GRC – Governance, Risk & ComplianceKI unter DORA für CISOs — BaFin guidance on ICT risksView whitepaper page →
 IT SecurityIoT Pentesting for CISOs — securing connected devices for realView whitepaper page →
 IT SecurityMagical 2FA Bypass — Effective MFA for CISOsView whitepaper page →
 Agentic AI SecurityAI OWASP LLM PenTesting: How to Truly Secure Your AI SystemsView whitepaper page →
 Agentic AI SecurityLLM Pentesting & Prompt Injection: How to Truly Protect AI Systems from ManipulationView whitepaper page →
 Agentic AI SecurityEU AI Act — Compliance Guide for CompaniesView whitepaper page →
 Agentic AI SecurityThreat-Model-Guided Security Testing for Agentic AI — Research EditionView whitepaper page →
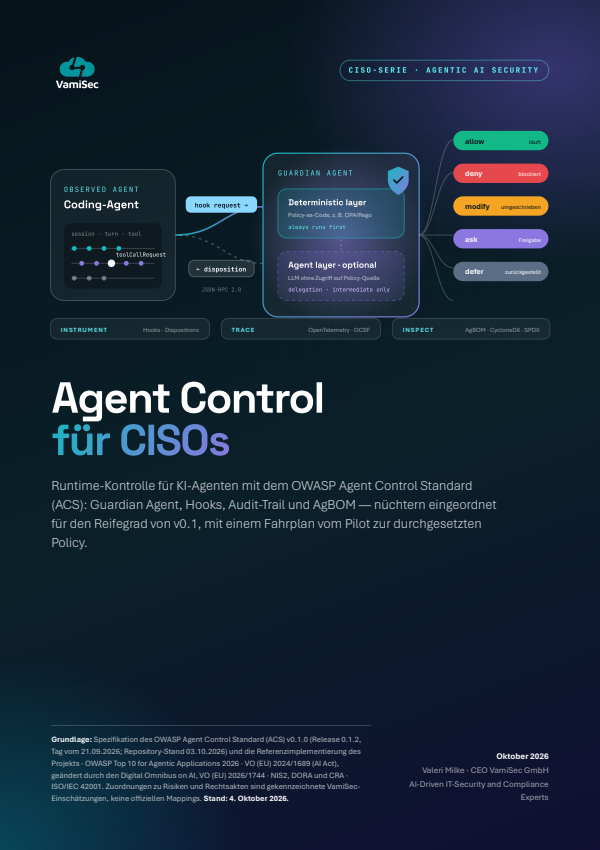 Agentic AI SecurityAgent Control for CISOs — OWASP Agent Control Standard (ACS)View whitepaper page →
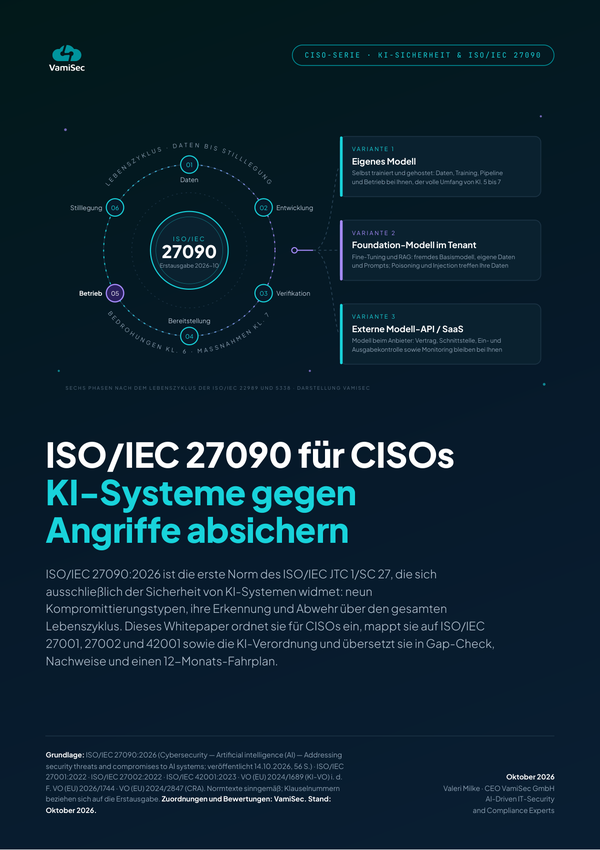 Agentic AI SecurityISO/IEC 27090 for CISOs — securing AI systems against attacksView whitepaper page →
 Agentic AI SecurityAutonomous Pentests for CISOs — the CSA Autonomous Pentest Assurance Standard (APAS)View whitepaper page →
 Agentic AI SecuritySecuring an MCP server in practice — Agent controls for CISOsView whitepaper page →
 Secure Software & Product DevelopmentEU Cyber Resilience Act — Practical guide for digital productsView whitepaper page →
 Secure Software & Product DevelopmentCI/CD Pipeline Security: How Attackers Take Over Your Pipeline — and How You Take It BackView whitepaper page →
 Secure Software & Product DevelopmentOWASP Top 10 CI/CD Security Risks — Practical Guide with Compliance CrosswalkView whitepaper page →
 Secure Software & Product DevelopmentSecure Coding in the AI Era: The CWE Top 25 (2025) and Secure-by-DesignView whitepaper page →
 Secure Software & Product DevelopmentAI-Powered Security in the CI/CD PipelineView whitepaper page →
 Secure Software & Product DevelopmentAutomotive Threat Matrix — ATT&CK for VehiclesView whitepaper page →
 Secure Software & Product DevelopmentSlopsquatting & Coding-Agenten für CISOs — securing the AI software supply chainView whitepaper page →
Looking for Individual Advice?
Our experts are happy to support you in implementing the content from our whitepapers in your organization.
Free Initial Consultation →