

it-sa 2026 recap: VamiGRC live at the BITMi stand, six demos and a dinner on the CRA reporting obligation
October 31, 2026
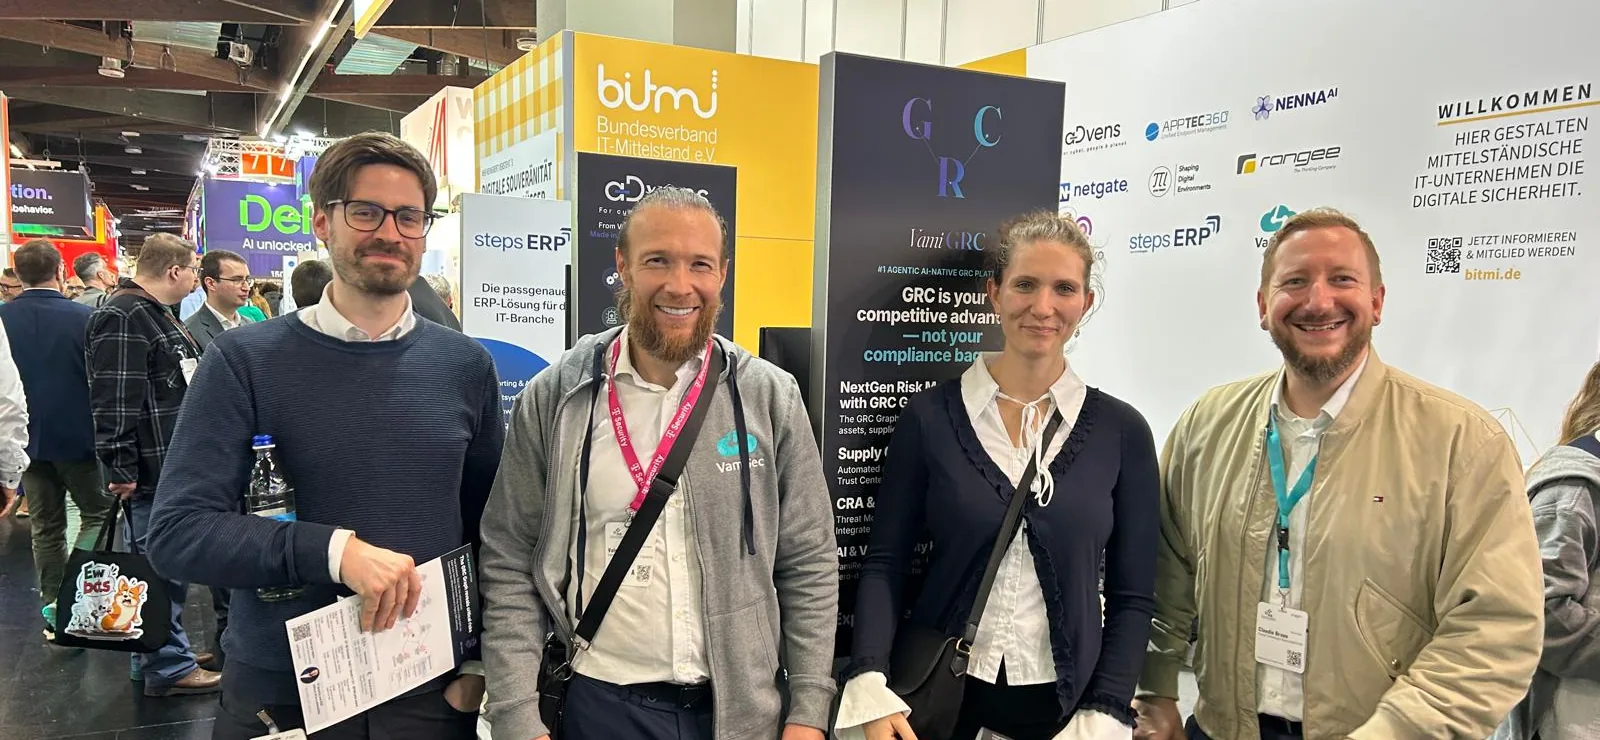
Three days in Nuremberg
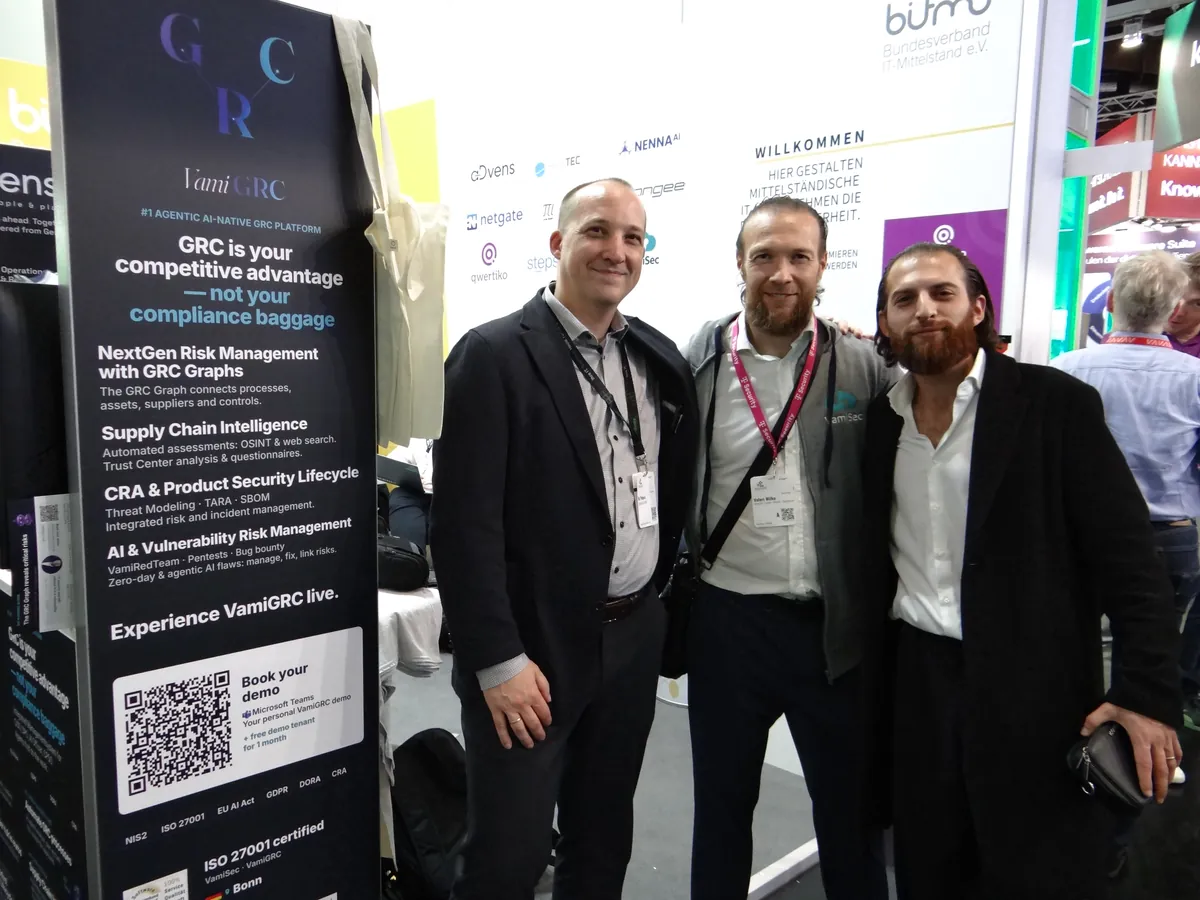
From October 27 to 29, 2026, VamiSec exhibited at it-sa Expo&Congress in Nuremberg, at booth 7-211 on the joint stand of the BITMi association. At the joint stand of the Bundesverband IT-Mittelstand in Hall 7, our focus was VamiGRC, our AI-native, agentic GRC platform – not on slides, but live on the system. Thank you to everyone who stopped by, to the team at the stand and to BITMi for organising the joint stand.
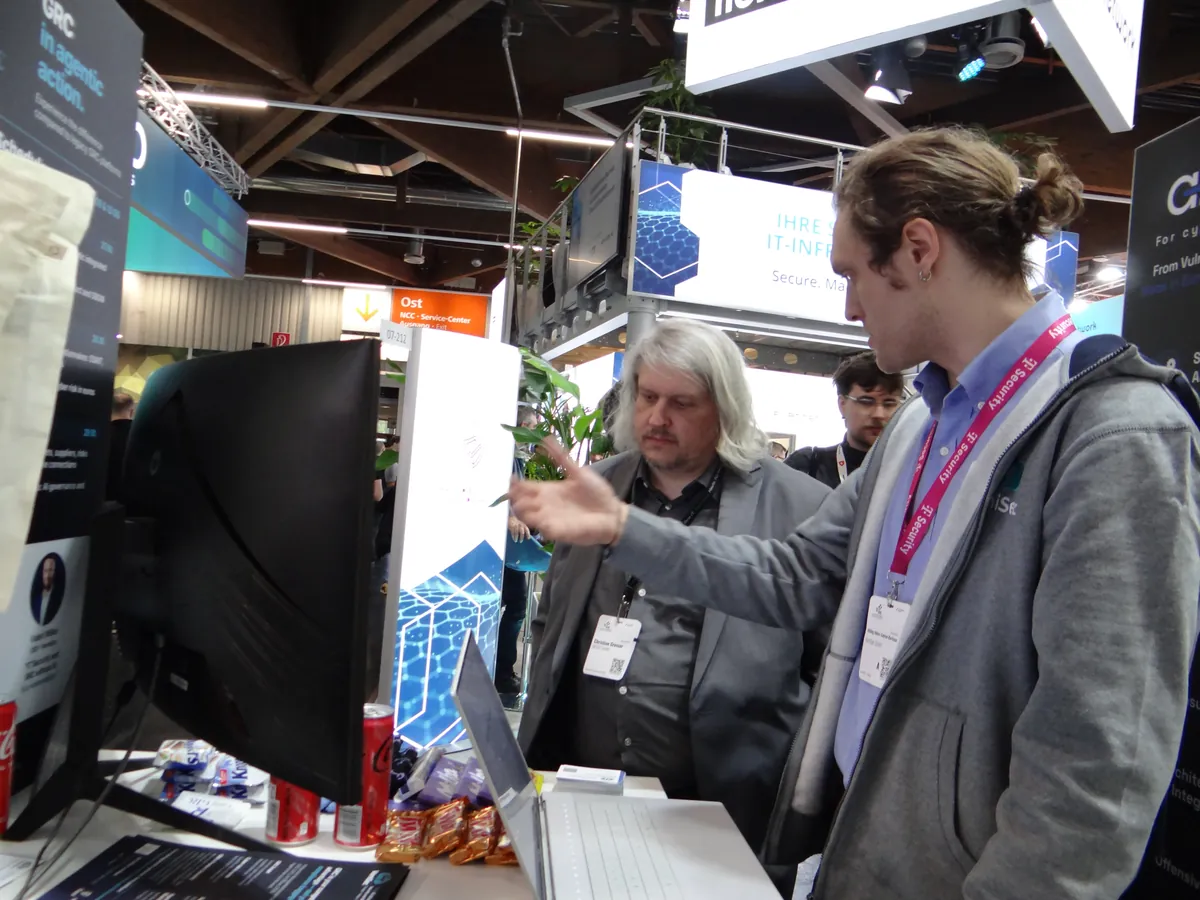
Six live demos: VamiGRC on the system instead of on slides
Twice a day, at 10:00 and 15:00, we showed in six live demos how VamiGRC handles typical governance, risk and compliance tasks: mastering NIS2, the CRA and the AI Act with an agentic integrated management system; the CRA reporting obligation from the product to the SBOM and the product security lifecycle; third-party risk management beyond questionnaires with OSINT, trust centres and automated assessments; quantitative risk management with cyber risks in euros and the ROSI; the GRC graph, which connects business processes, AI use cases, assets, suppliers, risks and controls; and AI governance from the use case to agents to ultimate accountability. The demo programme is still available on our it-sa page: https://vamisec.com/en/it-sa-2026#programm
What we talked about at the stand
Four topics shaped the conversations. First, implementing NIS2 and the Cyber Resilience Act, whose reporting obligation for actively exploited vulnerabilities has applied since September 11, 2026. Second, automating GRC: moving away from spreadsheets and slides towards a management system that connects requirements, risks, controls and evidence. Third, the security and compliance of AI systems under the AI Act, from AI agents to governance. And fourth, pentests and the external attack surface – a topic given extra urgency by the PHP2Shell and Brotli2Shell vulnerabilities disclosed shortly before the fair.
Dinner on October 28: what comes after the start of the CRA reporting obligation
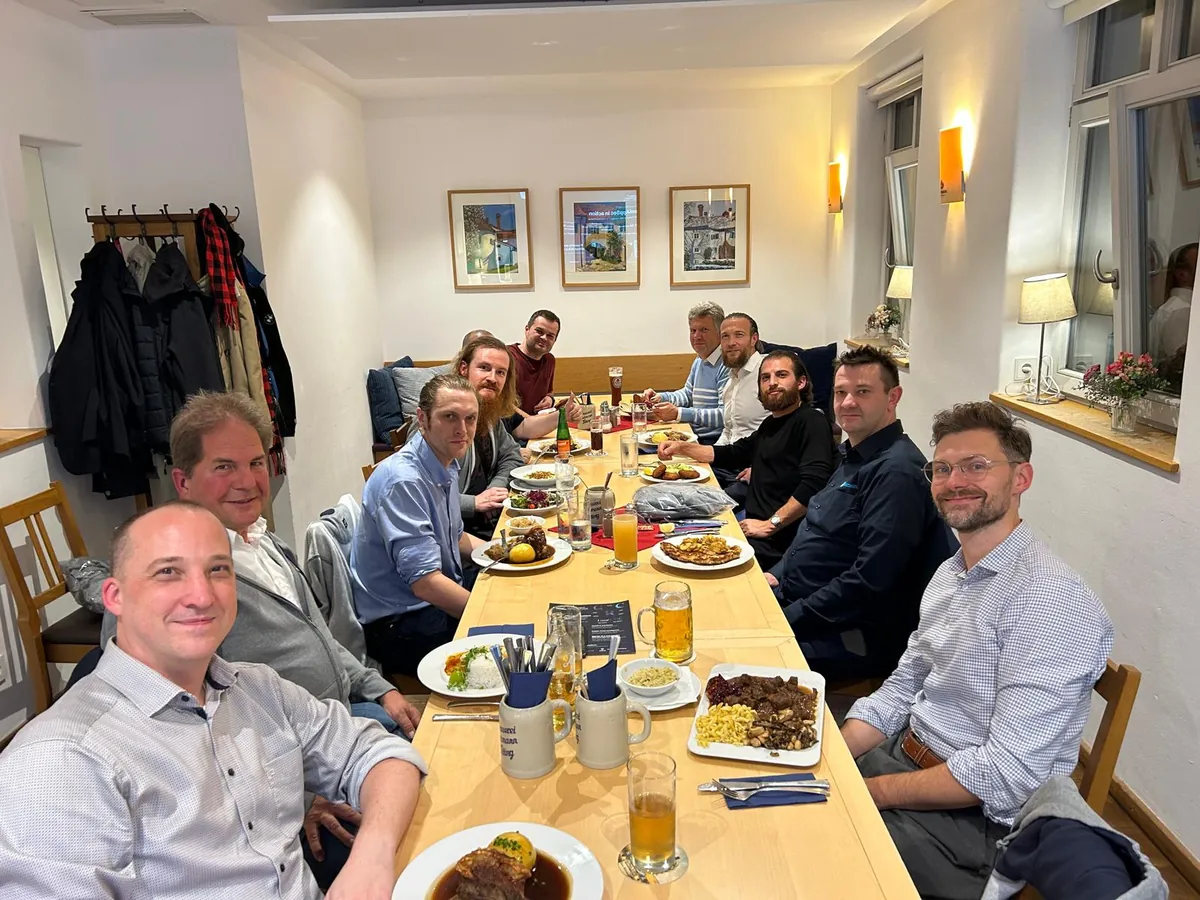
On Wednesday evening, customers and partners met for the VamiSec dinner at Gutmann am Dutzendteich in Nuremberg. The discussion topic was “The CRA reporting obligation is live – what comes next: from Security by Design via SBOM to the Product Security Lifecycle”. Thank you to all our guests for the open exchange.
Couldn't make it?
We are happy to show the demos online too, tailored to your questions. More on VamiGRC: https://vamisec.com/en/vamigrc and https://www.vamigrc.com/ · Until November 30 you can also request our Halloween special, a free 60-minute workshop on gap analysis, attack surface, threat modeling or an AppSec check: https://vamisec.com/en/news/halloween-special-2026 · All VamiSec events: https://vamisec.com/en/news?category=events
Impressions from it-sa 2026
Do you have questions about your organization's IT security?
Free Initial Consultation →