Book an Appointment
Halloween Special 2026

We shed light on your blind spots.
60-minute security workshop – free of charge.

This Halloween, we are treating you to an hour of expertise. You choose one of four focus areas: a quick gap analysis including document review, a technical analysis of your external attack surface with VamiRedteam, threat modelling with VamiThreat or a white-box application security check including an SBOM with VamiAppSec. We present the results to you in a management presentation – with concrete, prioritised measures.

  • 60 minutes
  • online
  • free of charge, no obligation
  • management presentation included
  • No scares: free of charge, with no follow-up commitment
  • Results as a management presentation for you to keep
  • Confidential – with an NDA on request
At a glance

One hour that brings clarity

VamiSec’s Halloween Special is a free, no-obligation 60-minute workshop for companies and organisations. You choose one focus area: a quick gap analysis including document review for NIS2, the CRA, DORA, ISO/IEC 27001, ISO/IEC 27090, ISO/IEC 27701 or ISO/IEC 42001, a technical analysis of your external attack surface with VamiRedteam, threat modelling with VamiThreat or a white-box application security check including an SBOM with VamiAppSec. VamiSec prepares the analysis and presents the results in the workshop as a management presentation with prioritised measures. Requests can be submitted until 30 November 2026.

Format
60 minutes online via video conference
Cost
Free of charge and without obligation
Focus area
One of four – your choice
Deliverable
Management presentation with action plan as a PDF
Audience
Companies and organisations, one workshop per organisation
Requests
By 30 November 2026, limited capacity
The four focus areas

Choose where we shine the light

Each focus area is tailored so that the preparatory analysis delivers meaningful results and the workshop can concentrate entirely on findings and measures.

01 · VamiSec consulting

Quick gap analysis including document review

How far along are you really? We review your existing documents and compare them with the framework of your choice – or with a sensible combination, such as ISO/IEC 27001 and NIS2.

What we analyse
  • Comparison of your documents with the core requirements of the chosen framework – for ISO/IEC 27090, with its recommendations
  • Implementation status per requirement area: implemented, partially implemented or open
  • Overlaps and synergies, so that you only need to provide evidence once
What you receive
Gap overview per requirement area and a prioritised roadmap with immediate measures
What we need from you
Your existing core documents, such as your information security policy, topic-specific policies, risk analysis or Statement of Applicability, and brief context on your company

ISO/IEC 27090 is guidance on the security of AI systems and is not certifiable – we use it as a benchmark for securing your AI applications.

02 · VamiRedteam

Technical analysis of your external attack surface

What does an attacker see when looking at your organisation from the internet? VamiRedteam maps your externally reachable systems – strictly within the authorised scope.

What we analyse
  • Domains and subdomains, reachable hosts, open ports and services
  • Publicly visible web applications, directories and interfaces (APIs)
  • Notable issues such as publicly reachable admin interfaces or forgotten test systems
What you receive
Overview of your external attack surface, findings with evidence and prioritised measures
What we need from you
Your written authorisation for the targets – domains and IP ranges over which you have authority

Non-invasive: we do not exploit any vulnerabilities and do not run load or DoS tests. Every agent action is checked against the authorised targets before execution.

03 · VamiThreat

Threat modelling with VamiThreat

For an application, cloud architecture or AI agent of your choice, we use VamiThreat to model where attacks could start – before they happen.

What we analyse
  • Data flow diagram with trust boundaries as a shared basis for the model
  • Threats according to STRIDE and, for agentic AI, MAESTRO from the Cloud Security Alliance
  • Mapping to MITRE ATT&CK and ATLAS, with attack path, risk and mitigation for each threat
What you receive
Prioritised threats with attack paths and concrete countermeasures
What we need from you
An architecture sketch, system description or existing documentation – as a Word document, PDF or diagram image

Particularly valuable before a release, a cloud migration or the deployment of AI agents.

04 · VamiAppSec

White-box application security check including SBOM

We examine the source code of an application of your choice from the inside – and deliver the software bill of materials (SBOM) along with it.

What we analyse
  • Static code analysis (SAST) and scanning for secrets in the code
  • Dependencies and open-source components (SCA) and, where present, infrastructure as code and containers
  • SBOM in CycloneDX or SPDX format, matched against actively exploited vulnerabilities (CISA KEV) and prioritised with EPSS
What you receive
Findings mapped to OWASP, the SBOM as a file and prioritised measures for your development team
What we need from you
Read access to a repository in GitLab, GitHub or Azure DevOps – or a code export

LLM of your choice: the local Qwen3.8 in VamiSec’s data centre in Sankt Augustin, Anthropic, OpenAI or your own model. No AI training on customer data.

Always included

Results made for executive management

Every workshop results in a management presentation: concise, easy to understand and with a clear basis for decision-making. You will receive the slides as a PDF afterwards.

  1. The big picture on one page

    Where you stand – easy to follow even without technical background knowledge.

  2. Findings by risk

    What really matters, prioritised by likelihood and impact.

  3. Action plan

    Immediate measures, the next 90 days and strategic steps.

  4. Effort and responsibility

    A rough estimate of the effort and who should take on what.

  5. Next steps

    What you can implement yourself – and where support makes sense.

VamiSec
Management presentationResults and measures
  • The big picture on one page
  • Findings by risk
  • Action plan
  • Effort and responsibility
  • Next steps
How it works

Five steps from your request to your measures

  1. 2 minutesSend your request

    Fill in the form and choose your focus area. We will get back to you promptly for the brief scoping call.

  2. about 15 minutesBrief scoping call

    We clarify the goal, scope and date – with an NDA on request. For technical analyses, we obtain your written authorisation.

  3. in advanceAnalysis by VamiSec

    We review your documents or carry out the analysis with VamiRedteam, VamiThreat or VamiAppSec. Your team only provides documents, authorisations or access.

  4. 60 minutes60-minute workshop

    Online via video conference: we present the results and answer your questions.

  5. afterwardsImplement measures

    You receive the management presentation as a PDF. Whether and how you proceed is up to you.

Fair and transparent

The terms

  • Free of charge and without obligation – no follow-up commitment, no subscription.
  • For companies and organisations, one workshop per organisation. Public bodies, please check in advance whether your rules allow you to accept a free service.
  • Requests accepted until 30 November 2026; the workshop itself may also take place afterwards. Capacity is limited: we allocate slots in the order in which requests are received. If it is exhausted, we will let you know.
  • Technical analyses only after written authorisation and only for systems over which you have authority.
  • The results are a first assessment based on your documents and the authorised scope. They make no claim to completeness and replace neither an audit nor a penetration test.
  • Confidential: with an NDA on request. Only the people you name receive the results.
  • VamiRedteam, VamiThreat and VamiAppSec run on T Cloud Public, exclusively in German data centres. We agree the language model with you – for example the local Qwen3.8 in VamiSec’s data centre in Sankt Augustin, or Anthropic or OpenAI. No AI training on customer data.
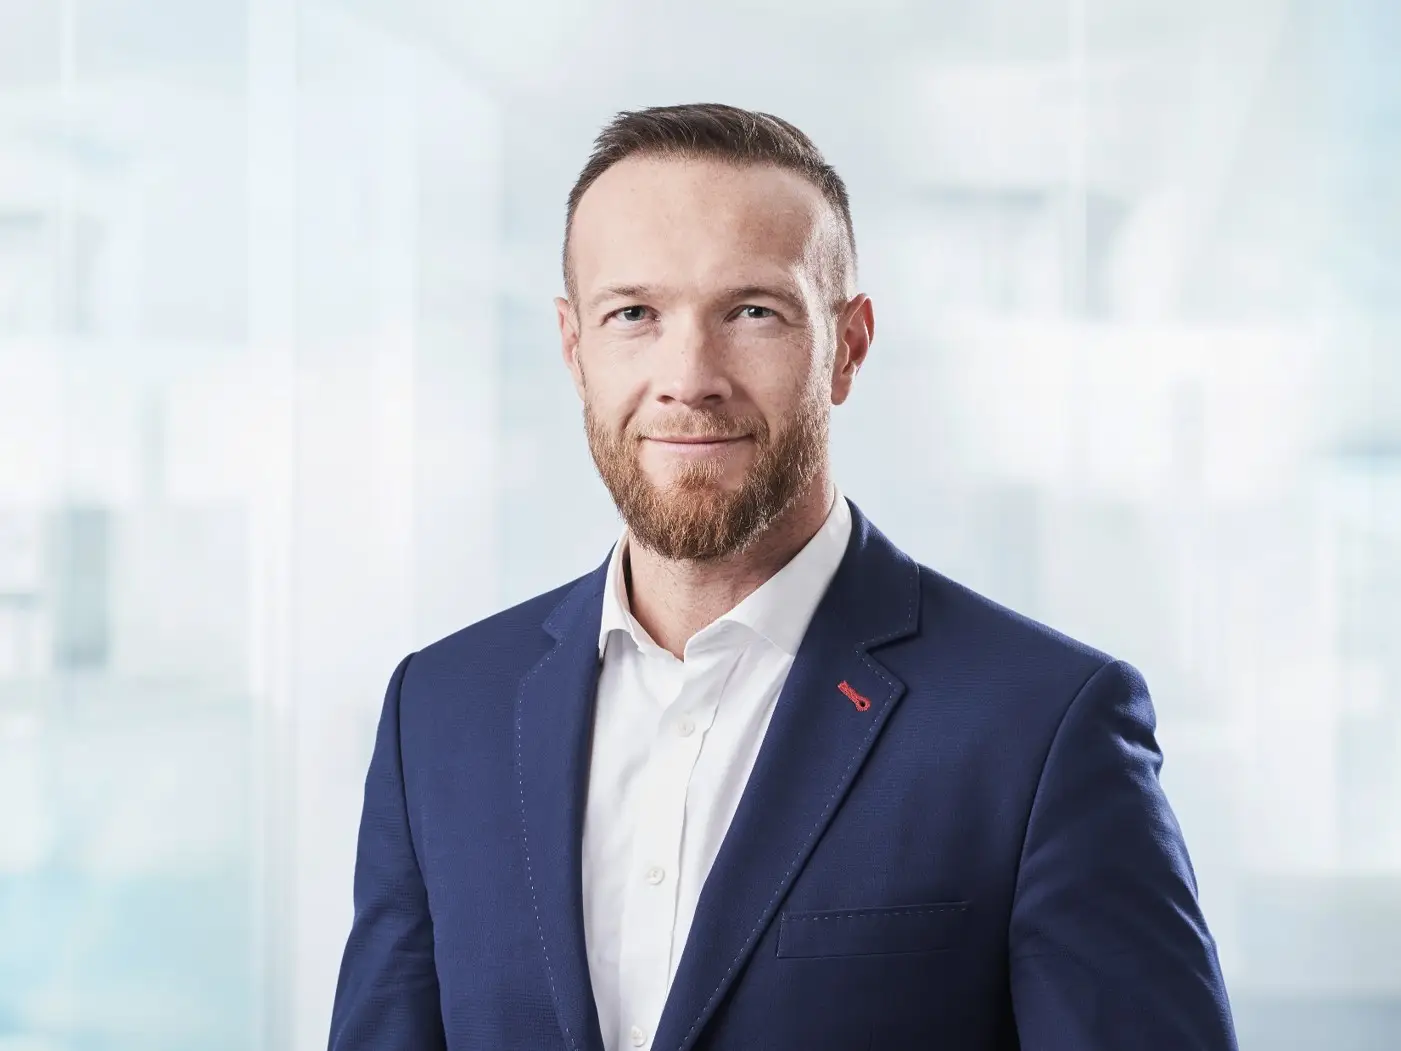
Valeri Milke, founder and managing director of VamiSec GmbH
Who is behind it

“IT security and compliance without AI is a vulnerability.”

VamiSec combines governance, risk & compliance with security testing and its own AI solutions. Founder and managing director Valeri Milke has worked in GRC, security testing and audit for 20 years. In the Halloween Special, you benefit from this experience – condensed into one hour.

Valeri MilkeFounder & Managing Director · VamiSec GmbHISO/IEC 27001 & ISO/IEC 42001 Lead Auditor
Request your workshop now
20years of GRC experience of our founder
4focus areas to choose from
60minute workshop
ISO 27001VamiSec itself is certified
Request

Secure your hour of expertise

A few details are enough. We will clarify the rest in the brief scoping call.

  • No scares: free of charge, with no follow-up commitment
  • Results as a management presentation for you to keep
  • Confidential – with an NDA on request

Prefer to talk directly? 30 minutes with Valeri Milke

Halloween SpecialRequest your free workshop

Required fields are marked with *. We will get back to you promptly for the brief scoping call.

Your focus area *

Your request goes to contact@vamisec.com.

Frequently asked questions

Good to know

Is the workshop really free of charge?

Yes. The preparatory analysis, the 60-minute workshop and the management presentation are free of charge and without obligation. A follow-up engagement is not a prerequisite.

How much effort is involved for our team?

Not much: a brief scoping call of about 15 minutes and the 60-minute workshop. We prepare the analysis. Depending on the focus area, you provide documents, written authorisation or read access.

Can I combine several focus areas?

You choose one focus area so that the hour is enough for meaningful results. For the gap analysis, a sensible combination is possible, such as ISO/IEC 27001 and NIS2. We are happy to discuss further topics afterwards.

Which documents do you need for the gap analysis?

Your existing core documents, such as your information security policy, topic-specific policies, risk analysis, Statement of Applicability and descriptions of roles and processes. If documents are missing, that in itself is an important finding.

Is the attack surface analysis a penetration test?

No. With VamiRedteam, we record non-invasively which of your organisation’s systems and services within the authorised scope can be reached from the internet. We do not exploit any vulnerabilities in the process. We offer penetration testing as a separate service.

Why do you need written authorisation?

We carry out even non-invasive analyses only with the consent of those who have authority over the systems. The authorisation defines the binding scope: every VamiRedteam agent action is checked against the authorised targets before execution.

What happens to our source code?

We use the access exclusively for the check and agree with you in advance on how the code is handled and deleted, with an NDA on request. VamiAppSec runs on T Cloud Public, exclusively in German data centres. You choose the language model: the local Qwen3.8 in VamiSec’s data centre in Sankt Augustin, Anthropic, OpenAI or your own model. We do not use customer data as training data.

Is ISO/IEC 27090 certifiable?

No. ISO/IEC 27090 is guidance on the security of AI systems. We use it as a benchmark to reveal gaps in how your AI applications are secured – often together with ISO/IEC 42001.

Who should attend the workshop?

Ideally a member of executive management and those responsible for the topic, such as the information security officer, CISO, head of IT or head of development. The management presentation is easy to follow even without technical background knowledge.

What is the deadline for requests?

Until 30 November 2026. The deadline applies to your request – we will arrange the workshop date together with you, and it may also be later. Capacity is limited: we allocate slots in the order in which requests are received. If it is exhausted, we will let you know.

What happens after the workshop?

You receive the management presentation with findings and prioritised measures as a PDF. Whether you implement the measures yourself or with us is your decision. On request, we will prepare a proposal.


All treats, no tricks

One hour of expertise.
Request it free of charge until 30 November.

Choose your focus area – we shed light on your blind spots and show you which measures are worth taking now.