Book an Appointment
Christmas workshop · by personal invitation

GRC Engineering
Christmas Workshop 2026

A Saturday for everyone who wants to build governance, risk and compliance rather than just administer it: in seven talks, Valeri Milke shows how NIS2, the CRA and the AI Act grow into one resilient system – from the integrated management system to supply chains and risk in euros to post-quantum cryptography.

10:00–15:00 CETVamiSec · Sankt Augustin near Bonn

No invitation yet? Request one

  • Free of charge
  • Lunch included
  • Max. 20 seats
NIS2CRAAI ActISO/IEC 42001SBOMTPRMROSIPQC & CBOM
At a glance

The workshop in 30 seconds

The GRC Engineering Christmas Workshop takes place on Saturday, 12 December 2026, from 10:00 to 15:00 CET at VamiSec, Bonner Straße 108, 53757 Sankt Augustin near Bonn, Germany. In seven talks, Valeri Milke, founder and managing director of VamiSec GmbH, shows how organisations implement NIS2, the Cyber Resilience Act and the AI Act in one integrated management system, make dependencies visible in a GRC graph, govern AI agents responsibly, quantify supplier and cyber risks in euros and prepare the migration to post-quantum cryptography. Attendance is free of charge, includes lunch and is by personal invitation only; seats are limited to 20.

What
In-person workshop with seven talks on GRC engineering
When
Saturday, 12 December 2026, 10:00–15:00 CET (arrival from 09:30)
Where
VamiSec, Bonner Straße 108, 53757 Sankt Augustin (near Bonn)
Speaker
Valeri Milke, founder and managing director of VamiSec GmbH
Audience
CISOs, information security officers, GRC, compliance and risk managers, product security
Cost
Free of charge, lunch and drinks included
Seats
Max. 20, by personal invitation only
Language
German; questions in English are welcome
Explained

What is GRC engineering?

GRC engineering applies principles from software and systems engineering to governance, risk management and compliance: requirements are modelled as structured data, controls are implemented once and evidenced many times, evidence is generated as automatically as possible, and dependencies between processes, systems, suppliers and risks become visible in a graph. The goal: compliance that grows with the organisation – instead of spreadsheets that start from scratch with every new regulation.

The workshop shows what this looks like in practice – vendor-neutral, with examples from real projects and with plenty of time for your questions.

  1. Requirements as data

    NIS2, the CRA, the AI Act, ISO/IEC 27001 and ISO/IEC 42001 are mapped to shared controls. One measure, several proofs.

  2. Dependencies as a graph

    Processes, assets, AI use cases, suppliers, risks and controls are connected – a graph reveals impacts before they become problems.

  3. Evidence as a by-product

    Evidence comes from day-to-day operations, not from the week before the audit. That saves time and makes statements verifiable.

  4. Agents with clear accountability

    AI agents take over the legwork such as research, matching and drafting. Approval and accountability stay with people.

The programme

Seven talks. Three blocks. One common thread.

The talks build on each other: first the foundation of management system and data model, then accountability for AI and products, finally the impact on the supply chain, risk assessment and cryptography. Each talk lasts about 30 minutes, including time for your questions.

All talks are given by Valeri Milke. Talks in German, questions in English are welcome. All times CET.

Block 1

Foundation

Management system and data model

Talk 1

Mastering NIS2, the CRA and the AI Act with an agentic integrated management system

Three regulations, many overlaps: risk management, supply chain, incident reporting, documentation. The talk shows how an integrated management system implements requirements once and evidences them many times, how ISO/IEC 27001 and ISO/IEC 42001 serve as a shared backbone – and where AI agents take over the legwork without taking over the accountability.

What you take away
  • A mapping approach that brings NIS2, the CRA and the AI Act onto shared controls
  • Where agents already help in the management system today – and where human approval remains mandatory
  • How to produce evidence that stands up to auditors and supervisors alike
Talk 2

Business processes, AI use cases, assets, suppliers, risks and controls: the GRC graph reveals the connections

Spreadsheets hide dependencies. A GRC graph links business processes, AI use cases, assets, suppliers, risks and controls into one searchable model. That way you answer questions such as “What happens if this supplier fails?” or “Which controls already cover this new requirement?” in minutes instead of meetings.

What you take away
  • A data model for the GRC graph that starts small and grows
  • Impact analyses across processes, suppliers and risks
  • How open formats such as OSCAL make frameworks machine-readable
Block 2

Accountability

AI governance and product security

Talk 3

From AI use cases to agents to risks: AI governance and ultimate accountability

Every AI agent needs an identity, clear permissions and an accountable person. The talk leads from the AI register through risk assessment to approval and shows how the AI Act, ISO/IEC 42001 and human-in-the-loop work together in daily operations. The AI Act’s transparency obligations have applied since August 2026; obligations for high-risk systems follow in stages from December 2027.

What you take away
  • An AI register that connects use cases, models, agents and owners
  • Risk assessment and approval for agentic systems with human-in-the-loop
  • What management needs to know to carry ultimate accountability
Talk 4

The CRA reporting obligation is live – what now? From the product to the SBOM to the product security lifecycle

Since 11 September 2026, manufacturers have had to report actively exploited vulnerabilities and severe security incidents. The talk follows the path from the product via the SBOM to the report and shows what a product security lifecycle looks like that carries you through to full application of the Cyber Resilience Act in December 2027.

What you take away
  • Early warning within 24 hours, notification within 72 hours, final report: processes that hold up in an emergency
  • The SBOM as the basis for vulnerability management and reporting
  • Building blocks of a product security lifecycle for 2027
Block 3

Impact

Supply chain and risk in euros

Talk 5

Third-party risk management beyond questionnaires: OSINT, trust centers and automated assessments

Questionnaires show what suppliers say about themselves – not what things actually look like. The talk combines OSINT signals, trust centers and automated assessments into third-party risk management that stands up to NIS2 and DORA. Criticality ratings and decisions remain with you.

What you take away
  • Tier suppliers by criticality and align the assessment effort accordingly
  • Use OSINT and trust centers to complement questionnaires
  • Automated assessments with traceable reasoning
Talk 6

Quantitative risk management: assessing cyber risks in euros and calculating ROSI

Traffic-light colours don’t convince a board. The talk translates cyber risks into euro ranges, shows how to estimate likelihood and impact robustly, and derives the return on security investment so that investment decisions become traceable.

What you take away
  • From traffic lights to euro ranges: estimating with ranges instead of false precision
  • Deriving and presenting ROSI transparently
  • Risk reports that fit into budget discussions
Christmas special
Mastering post-quantum cryptography: creating visibility with the CBOM

Harvest now, decrypt later, a crypto inventory with the CBOM and a realistic roadmap for the migration.

To the PQC special
Christmas special · Talk 7

Mastering post-quantum cryptography: make it visible first, then migrate

Encrypted data intercepted today could be decrypted by future quantum computers. The EU member states have therefore agreed on a joint roadmap: the transition to post-quantum cryptography is to begin by the end of 2026. Yet hardly any organisation knows exactly where which cryptography is in use. This is where the CBOM comes in – the cryptography bill of materials.

  • Harvest now, decrypt later: which data is already at risk today and how to set priorities with Mosca’s theorem
  • Visibility with the CBOM: inventory algorithms, keys, certificates and protocols in the open CycloneDX standard
  • From inventory to roadmap: crypto-agility, hybrid schemes and the NIST standards ML-KEM and ML-DSA
  • Crypto assets in the GRC graph: linked to systems, suppliers, risks and controls – so that PQC does not remain an isolated project
The schedule

Saturday, 12 December 2026

  1. Arrival with coffee and Christmas biscuitsArrival
  2. Welcome and introduction: what GRC engineering is aboutOpening
  3. Talk 1: NIS2, CRA and AI Act in an agentic integrated management systemBlock 1
  4. Talk 2: the GRC graphBlock 1
  5. Coffee breakBreak
  6. Talk 3: AI governance and ultimate accountabilityBlock 2
  7. Talk 4: CRA reporting, SBOM and product security lifecycleBlock 2
  8. Lunch and conversationLunch
  9. Talk 5: third-party risk management beyond questionnairesBlock 3
  10. Talk 6: quantitative risk management and ROSIBlock 3
  11. Talk 7 – Christmas special: post-quantum cryptography with the CBOMSpecial
  12. Questions, discussion and outlook for 2027Q&A
  13. End of the workshop
Confirm attendance
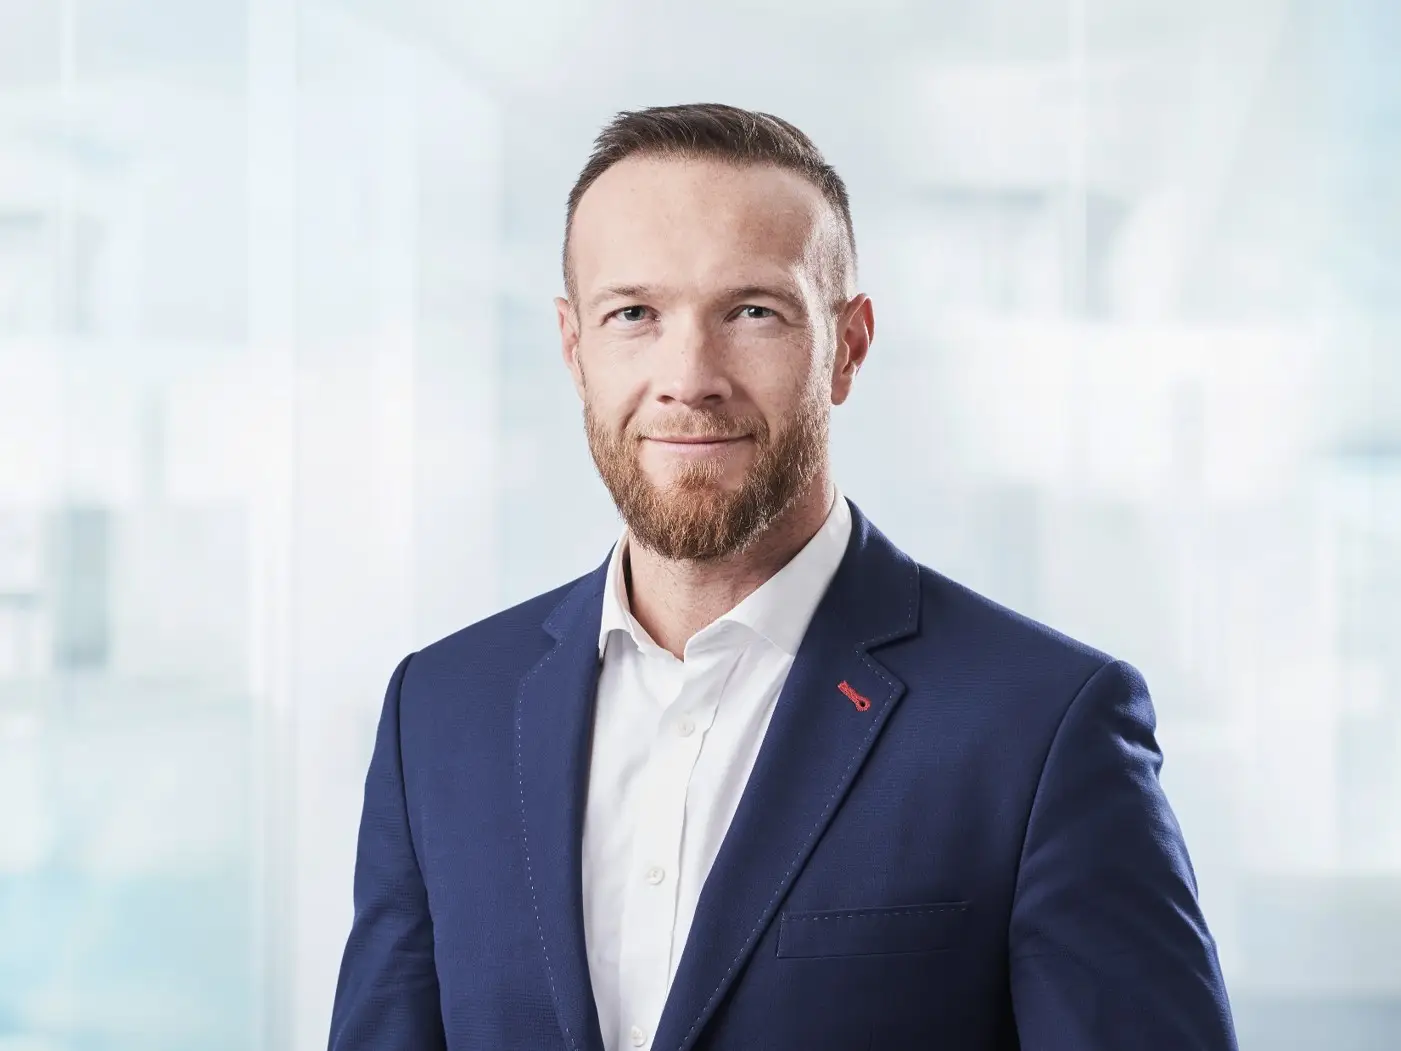
Valeri Milke, founder and managing director of VamiSec GmbH
Your speaker

“IT security and compliance without AI is a vulnerability.”

Valeri Milke has worked in governance, risk & compliance, security testing and audit for 20 years. As founder and managing director of VamiSec GmbH, he supports organisations with NIS2, the CRA, the AI Act and ISO certifications – and gives all seven talks of the workshop himself. His aim: methods that still work on the Monday after.

Valeri MilkeFounder & Managing Director · VamiSec GmbHISO/IEC 27001 & ISO/IEC 42001 Lead Auditor
Confirm attendance
20years of GRC experience
7talks on one Saturday
20seats for real discussion
ISO 27001certified company
Who is it for?

For everyone who wants to build compliance, not just administer it

  • CISOs & information security officers
  • GRC & compliance
  • Risk management
  • Product security & PSIRT
  • Procurement & supplier management
  • AI officers
  • Data protection
  • Internal audit
  • IT management & executives
Venue

VamiSec in Sankt Augustin near Bonn

The workshop takes place at VamiSec’s premises in Sankt Augustin, a few kilometres north-east of Bonn, Germany. With a maximum of 20 participants, there is room for questions, discussion and conversations over lunch.

  • A few minutes from Bonn, around 30 kilometres south-east of Cologne
  • Details on getting there and parking come with your seat confirmation
  • Arrival from 09:30 with coffee and Christmas biscuits
Address
VamiSec
Bonner Straße 108
53757 Sankt Augustin
Plan your route
Attend

By personal invitation only

The workshop is deliberately small: we personally invite a maximum of 20 participants. Have you received an invitation? Then confirm your attendance here. No invitation, but you would like to join? Request an invitation – we will get back to you personally.

  1. 1
    Confirm or request

    Confirm with your personal invitation, or request one if you don’t have one yet.

  2. 2
    Personal confirmation

    Your seat is reserved as soon as we confirm it by email.

  3. 3
    Join us on 12 December

    Arrival from 09:30, start at 10:00 in Sankt Augustin.

Questions in advance? contact@vamisec.com

Confirmation & invitation requestGRC Engineering Christmas Workshop · 12 Dec 2026

Required fields are marked with *. Please do not enter confidential information.

Your request *

Your message goes to the VamiSec team at contact@vamisec.com.

Good to know

Frequently asked questions about the workshop

What is GRC engineering?

GRC engineering applies engineering principles to governance, risk management and compliance: requirements are modelled as data, controls are implemented once and evidenced many times, evidence is generated as automatically as possible, and dependencies between processes, systems, suppliers and risks become visible in a graph.

When and where does the workshop take place?

On Saturday, 12 December 2026, from 10:00 to 15:00 CET at VamiSec, Bonner Straße 108, 53757 Sankt Augustin, a few kilometres north-east of Bonn, Germany. Arrival is possible from 09:30.

How can I attend?

Attendance is by personal invitation only. If you have an invitation, confirm your attendance using the form on this page. If you don’t, you can request an invitation there – we will get back to you personally.

How much does it cost?

Nothing. The workshop is free of charge, lunch and drinks are included.

How many seats are there?

A maximum of 20. The small group is intentional: it leaves time for questions and discussion in every talk.

Who gives the talks?

All seven talks are given by Valeri Milke, founder and managing director of VamiSec GmbH, ISO/IEC 27001 and ISO/IEC 42001 Lead Auditor with 20 years of experience in governance, risk & compliance.

Which topics does the workshop cover?

NIS2, the CRA and the AI Act in an integrated management system, the GRC graph, AI governance, the CRA reporting obligation with SBOM and product security lifecycle, third-party risk management, quantitative risk management with ROSI and, as a Christmas special, post-quantum cryptography with the CBOM.

Is the workshop vendor-neutral?

Yes. The focus is on methods, regulations and practical experience – not on a specific product.

What language are the talks in?

German. You are welcome to ask questions in English.

Do I need prior knowledge?

Basic knowledge of information security, compliance or risk management helps. The talks build on each other and start with the foundation.

How do I get to the venue?

VamiSec, Bonner Straße 108, 53757 Sankt Augustin, Germany. “Plan your route” opens directions in Google Maps; details on getting there and parking come with your seat confirmation.


GRC Engineering Christmas Workshop · 12 Dec 2026

Seven talks. Twenty seats.
A Saturday’s head start on 2027.

Free of charge, with lunch, in Sankt Augustin near Bonn – by personal invitation only.